the IETF's Supply Chain Integrity, Transparency and Trust working group - an architecture for append-only transparency registries where issuers publish signed statements about artifacts and verifiers check registry receipts.
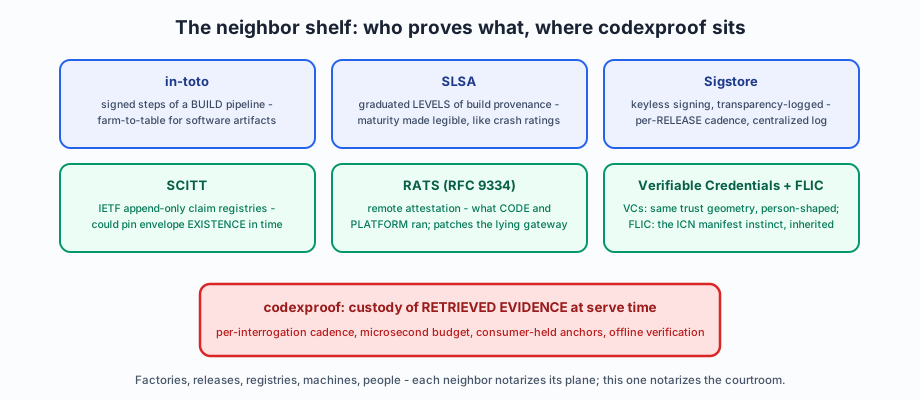
The shelf: SCITT's registries could pin envelope existence in time - the composition that closes the backdating edge.
Etymology and backstory
chartered at the IETF in 2022-2023 to generalize the certificate-transparency trick (public append-only logs forcing honesty) beyond certificates to arbitrary supply-chain claims - SBOMs, attestations, audit statements. COSE-signed statements, Merkle-tree registries, receipts as inclusion proofs.
Ecosystem
early adopters in firmware and critical-infrastructure supply chains; the standards-track sibling of Sigstore's Rekor log.
In codexproof
cited as the transparency-layer neighbor and a natural future composition: SCITT-style receipts could give codexproof envelopes third-party existence proofs (this envelope was registered at time T), patching the one thing self-contained verification cannot prove alone - that an artifact existed before a given moment. The paper's external-timestamping gap (Q19's backdating edge) is exactly SCITT-shaped.