Supply-chain Levels for Software Artifacts - Google's graduated framework (levels 1 through 3+) specifying how much provenance and build integrity an artifact carries, from "provenance exists" to "hardened, unfalsifiable builds."
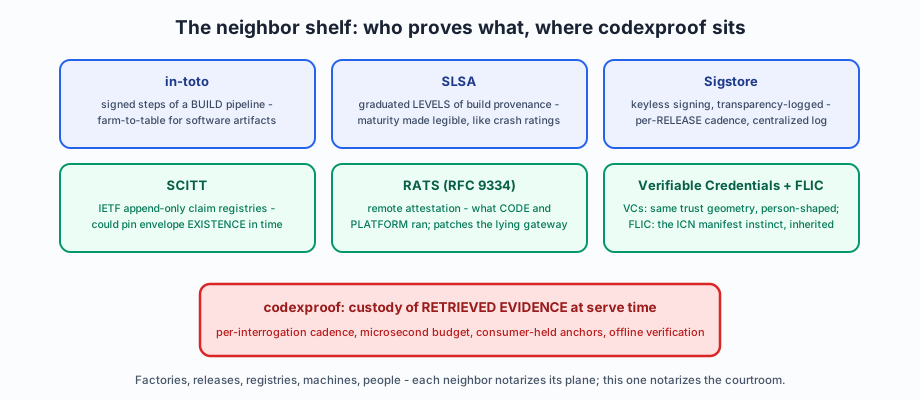
The shelf: SLSA grades the factory's provenance; the red box grades nothing - it verifies serve-time custody.
Etymology and backstory
pronounced salsa; grew from Google's internal Binary Authorization for Borg practices, published as an open framework in 2021 under the OpenSSF after SolarWinds made supply-chain compromise a boardroom word. The level system did for provenance what seatbelt ratings did for cars: made maturity legible and purchasable.
Ecosystem
GitHub and GitLab emit SLSA provenance; package registries verify it; procurement checklists ask for levels. The de facto vocabulary of software supply-chain policy.
In codexproof
cited as the maturity-model neighbor. SLSA grades the trustworthiness of BUILD provenance; codexproof's trust schema and revocation grade the authority behind EVIDENCE provenance at serve time. The rhyme worth saying in a consulting room: SLSA levels are to build pipelines what consumer-chosen anchors plus mandatory freshness are to evidence pipelines - graduated, checkable trust.