a hierarchical name prefix that scopes authority - in codexproof, the slash-delimited prefix a domain owns, under which all its data names and signer names must nest.
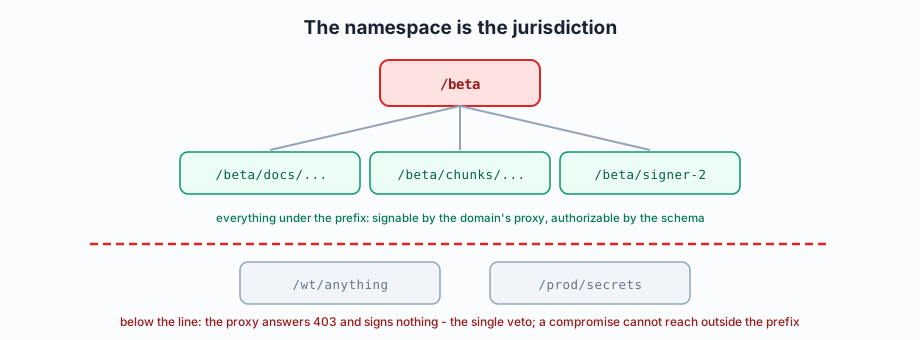
The jurisdiction as a tree: everything above the dashed line signable, everything below refused.
Etymology and backstory
namespaces are one of computing's oldest disciplines (file paths, DNS labels, programming-language scopes), but their use as a SECURITY boundary is the NDN inheritance: when names are hierarchical and signed, prefix containment becomes a checkable claim of jurisdiction. DNS pioneered global hierarchical delegation; NDN moved the same shape into the data plane.
Ecosystem
DNS zones, Kubernetes namespaces, AWS ARN prefixes, NDN name trees - the same idea at different layers: authority scoped by prefix.
In codexproof
each signing proxy is namespace-pinned via PROV_NAMESPACE and refuses (HTTP 403) to sign any template whose names fall outside its pin - the single veto in the signing path. The trust rule's prefix-containment check is the verifier-side mirror of the same discipline. Blast radius of a domain compromise = its namespace, exactly (Q19).